Google Uncovers New Malware Linked to Russian Hacking Group Cold River
 Isabella Alexiou
08 May 2025

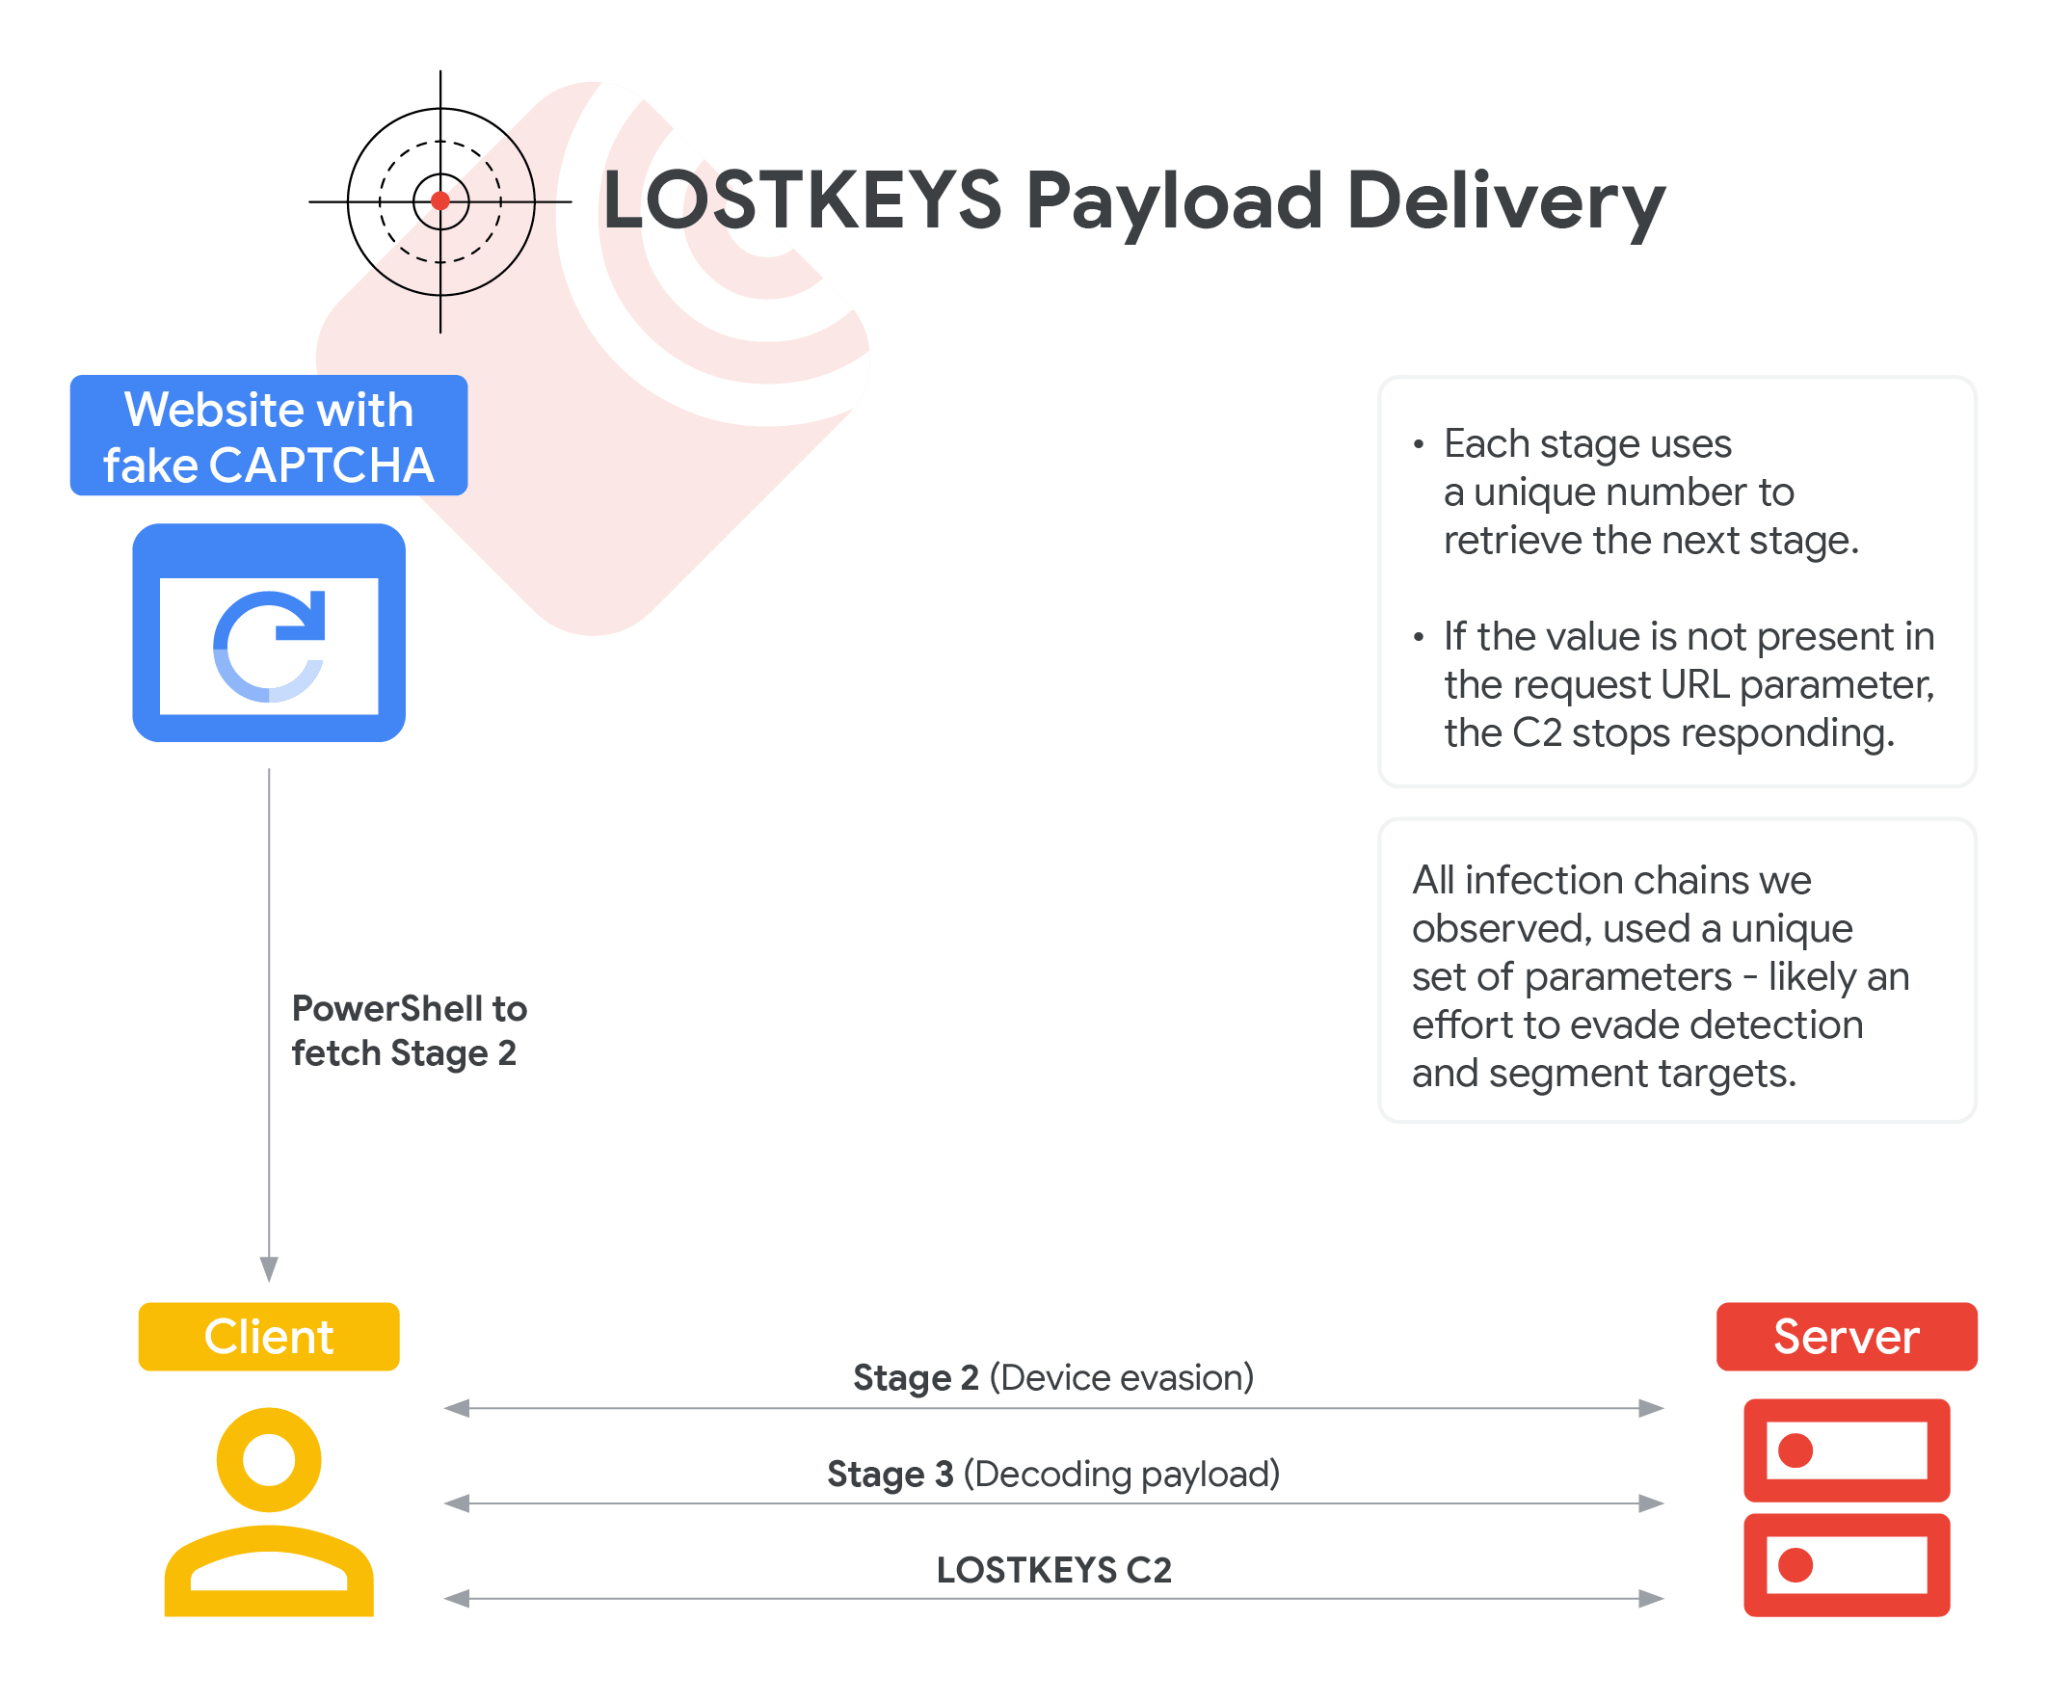
Google has identified a new strain of malware, dubbed “LOSTKEYS,” linked to Cold River, a Russian-based hacking group previously tied to the country’s Federal Security Service.
In a blog post published Wednesday, Wesley Shields from Google’s Threat Intelligence Group described LOSTKEYS as a “new development in the toolset” of the group, which is known for conducting espionage campaigns targeting high-profile Western entities.
The malware is capable of stealing files and transmitting system information back to attackers.
Cold River has a history of targeting NATO governments, NGOs, intelligence officials, and diplomats.
Google said that between January and April this year, the group aimed its efforts at current and former advisers to Western governments and militaries, journalists, think tanks, and individuals with connections to Ukraine.
The discovery highlights Cold River’s ongoing efforts to collect intelligence in support of Russian strategic interests.
Google previously linked the group to significant attacks, including a 2022 campaign targeting three U.S. nuclear research laboratories and the leak of private emails belonging to former British intelligence chief Richard Dearlove.
The Russian embassy in Washington has not commented on the latest findings.