Google Takes Down Massive Android Botnet Infecting 1.3 Million Devices
 Dominic Bayley
03 Nov 2026
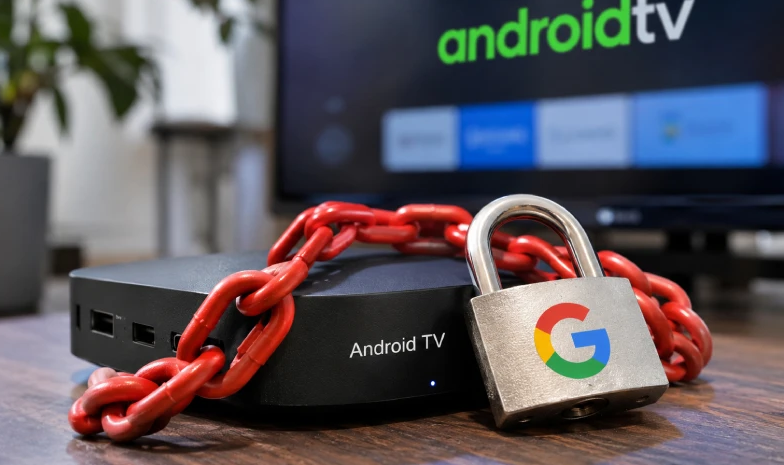
Google has dismantled a massive botnet that infected more than 1.3 million Android devices worldwide, including thousands in Australia, after discovering that a Chinese manufacturer allegedly installed malicious software in TV set-top boxes before they were sold.
The operation targeted a backdoor known as x.cpe, which Google claims was deliberately embedded in devices manufactured by Shenzhen-based Videostrong, allowing cybercriminals to secretly access consumers’ home internet connections.
Google says it is highly confident the manufacturer intentionally installed the software and sold access to criminal operators, rather than the infections resulting from a security mistake or rogue employee.
The compromised devices were primarily Android TV set-top boxes, although researchers also identified infections in karaoke machines, digital signage equipment and telehealth devices.
According to cybersecurity company TrendAI, researchers identified 1,472,554 infected devices across 206 models between June and October 2026.
Australia was among the affected markets, with an estimated 26,000 to 42,000 compromised devices. Similar infection levels were reported in the United States, Germany, the United Kingdom and Canada.
Malaysia, Brazil, Iraq, Mexico and Taiwan recorded some of the highest concentrations of infected devices.
The malware operated at the firmware level, giving attackers extensive control over infected equipment without the owner’s knowledge.
Once activated, the backdoor could disable Google Play Protect security checks, install additional malicious applications, capture screenshots, record keystrokes and extract account information.
Researchers also discovered that attackers could execute remote commands and investigate other devices connected to the same home network.
Much of the criminal activity involved converting compromised devices into residential proxies, allowing third parties to route internet traffic through unsuspecting households.
This made malicious activity appear to originate from legitimate residential internet connections, potentially concealing the identity and location of cybercriminals.
Other malware modules were used to generate fraudulent advertising views and monetise unused internet bandwidth.
Google worked with Japan’s National Police Agency and cybersecurity organisations including Lumen, HUMAN Security, Plume, Synthient and TrendAI to disrupt the operation.
The coordinated takedown, conducted in late October, disabled domains and command-and-control infrastructure used to manage the infected devices.
Google also targeted infrastructure associated with more than a dozen additional malware families distributed through the backdoor.
The company believes the disruption could affect criminal access to at least 10 million additional infected devices.
However, the takedown does not remove the malicious software already installed on consumers’ equipment.
Because x.cpe is embedded in system firmware and operates with elevated privileges, conventional antivirus tools and factory resets may not permanently eliminate the infection.
Security researchers warn that the backdoor can reinstall itself when an affected device restarts.
Cybersecurity firm Synthient identified 182 device model names associated with the campaign, although it cautioned that a matching model name does not necessarily mean a particular device is infected.
Its investigation focused partly on MECOOL-branded Android TV boxes, including a KM9PRO Max purchased by researchers that contained the preinstalled backdoor.
Google has now severed its relationship with Videostrong, banning the manufacturer and its future subsidiaries or affiliates from producing or selling certified Android devices or supplying software to certified manufacturers.
For consumers, the findings raise concerns about the security of inexpensive Android TV boxes and other connected products sold through online marketplaces.
Researchers recommend disconnecting confirmed infected devices and replacing them rather than relying on a factory reset.
Businesses are also being urged to isolate potentially compromised smart devices from sensitive networks and ensure employees use managed equipment when accessing corporate systems.
Although Google’s intervention has disrupted the botnet’s infrastructure, researchers warn that criminal operators could establish replacement systems, leaving infected devices vulnerable to further exploitation.