Google Bans Android TV Box Maker After Malware Found On 1.3 Million Devices
 April Ossington
06 Nov 2026

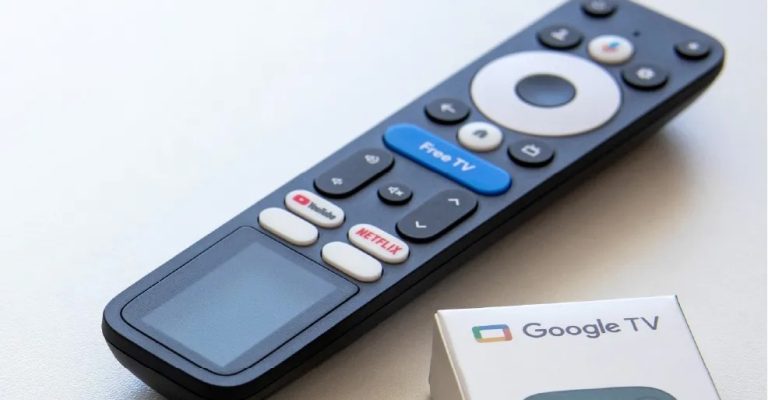
Google has taken action against an Android TV box manufacturer after malware was found running on more than 1.3 million set-top boxes, including devices that had previously passed the company’s Play Protect certification process.
The malware, known as XCPE or x.cpe, was built into the firmware of a range of Android TV devices over several years, according to Google’s Threat Intelligence Group.
Google traced the operation to Shenzhen-based Videostrong Technology, which manufactures Android devices under its own brands and for third parties. Many of the affected products were reportedly sold under the Mecool name.
Google said it had assessed with high confidence that the backdoor and associated botnet were intentionally developed, deployed and operated by Videostrong for financial gain.
Once activated, the malware enrolled affected devices into a botnet and allowed access to be sold to criminal groups. Those groups could then use household internet connections for activities including advertising fraud and residential proxy services.
The malware could also install additional malicious software, disable Google Play Protect, run remote commands, capture screenshots and scan other devices connected to the same home network.
Google said it observed operators taking live screenshots from compromised devices and stealing account information.
The case is particularly significant because many of the affected products were certified Android TV devices. Google has previously advised consumers to choose Play Protect-certified hardware as a safer alternative to uncertified Android boxes running the Android Open Source Project.
According to Google, the malicious code avoided detection during certification because it was downloaded only after the television box had completed setup and connected to the internet.
The company said it has since changed its certification and security processes to address the gap.
Google also pursued legal and technical action against infrastructure used to control the botnet. Servers linked to XCPE and more than a dozen other malware families were taken down as part of the operation.
Google estimates the action has also disrupted access to at least 10 million additional compromised devices.
Japan’s National Police Agency and security companies including Lumen, Human Security, Plume, Synthient and TrendAI were involved in the response.
Videostrong has now been blocked from producing certified Android devices and from supplying software to other vendors participating in Google’s certification program.
However, removing the malware from existing devices is more complicated.
According to security researchers, the backdoor can reinstall itself from a protected system partition after being deleted. Installing clean firmware or disconnecting the device from the internet may therefore be necessary to prevent further activity.
Synthient has identified 182 model names associated with devices observed carrying the XCPE backdoor, although researchers have cautioned that a matching model number alone does not necessarily mean a particular device is infected.
Trend Micro counted 1,472,554 compromised devices, with large numbers detected in Brazil, Malaysia, Iraq, Mexico and Taiwan. Infected units were also identified in Australia, the United States, Germany, the United Kingdom and Canada.
The incident raises fresh questions around the security of low-cost Android TV hardware, particularly products sold under lesser-known brands or through manufacturers that supply multiple third-party labels.
It also demonstrates that certification alone may not guarantee a device remains secure after it leaves the factory, particularly if software can be changed after setup.
For consumers, the case adds another reason to consider the manufacturer and its security track record when choosing a streaming device, rather than relying solely on certification branding.