Major French Supermarket Cyberattack Targets Fridges, Costing Millions & Sparking Fires
 Emma Wheaton
13 Oct 2026
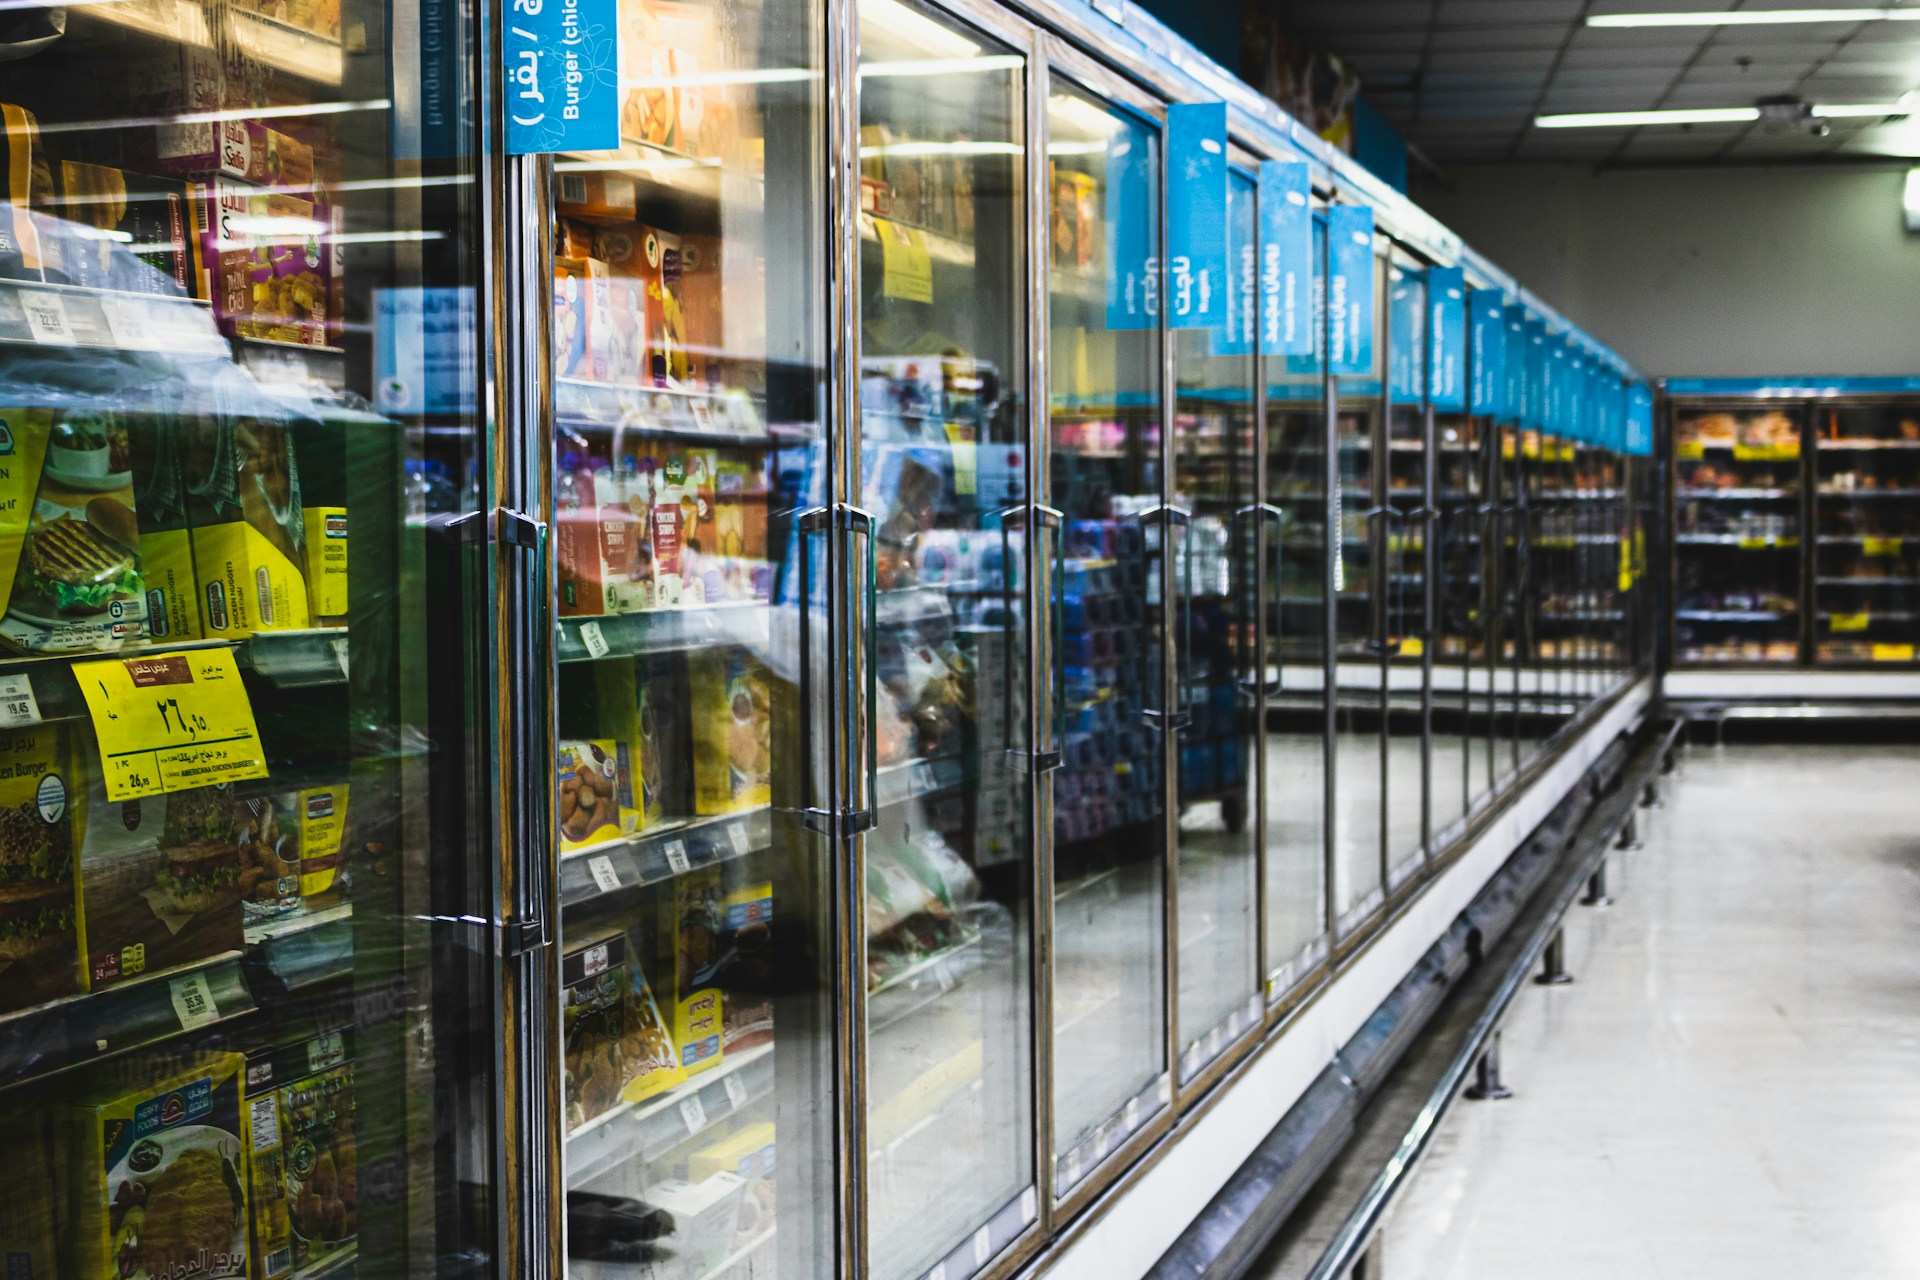
Hackers have remotely manipulated refrigeration systems at hundreds of French supermarkets, forcing temperatures in fridges and freezers to climb as high as 50 degrees Celsius, spoiling food stock and triggering fires.
Authorities are investigating the major cyberattack which hit several major retail chains in France and has exposed the risks of internet-connected refrigeration. It has raised questions about the security of the operational technology used to run essential retail infrastructure.
France’s National Cybersecurity Agency (ANSSI) is reportedly working to identify the vulnerability and determine whether businesses elsewhere in Europe could also be affected.
Intermarché reported that around 150 stores were affected, with refrigeration temperatures reportedly reaching 50 degrees for approximately six hours overnight. The retailer said compromised fresh and frozen food had to be thrown away.
Carrefour confirmed that 80 of its supermarkets were also hit, while Monoprix reported that approximately 5% of its roughly 490 French stores were affected. Cooperative U also confirmed that its refrigeration systems had been targeted.
Other retailers, including E.Leclerc, reported or were linked to disruptions, although the extent of the impact varied.
Intermarché’s chief executive, Thierry Cotillard, warned that the financial losses could reach tens of millions of euros nationwide in a single day.
The Paris prosecutor’s office has confirmed an investigation into the large-scale attack, including the damage caused by food losses and reports of fires at affected locations.
Modern supermarket refrigeration systems are often connected to networks for technicians to monitor and make adjustments to controls, such as temperatures, remotely. However, that connectivity can also create an entry point for attackers.
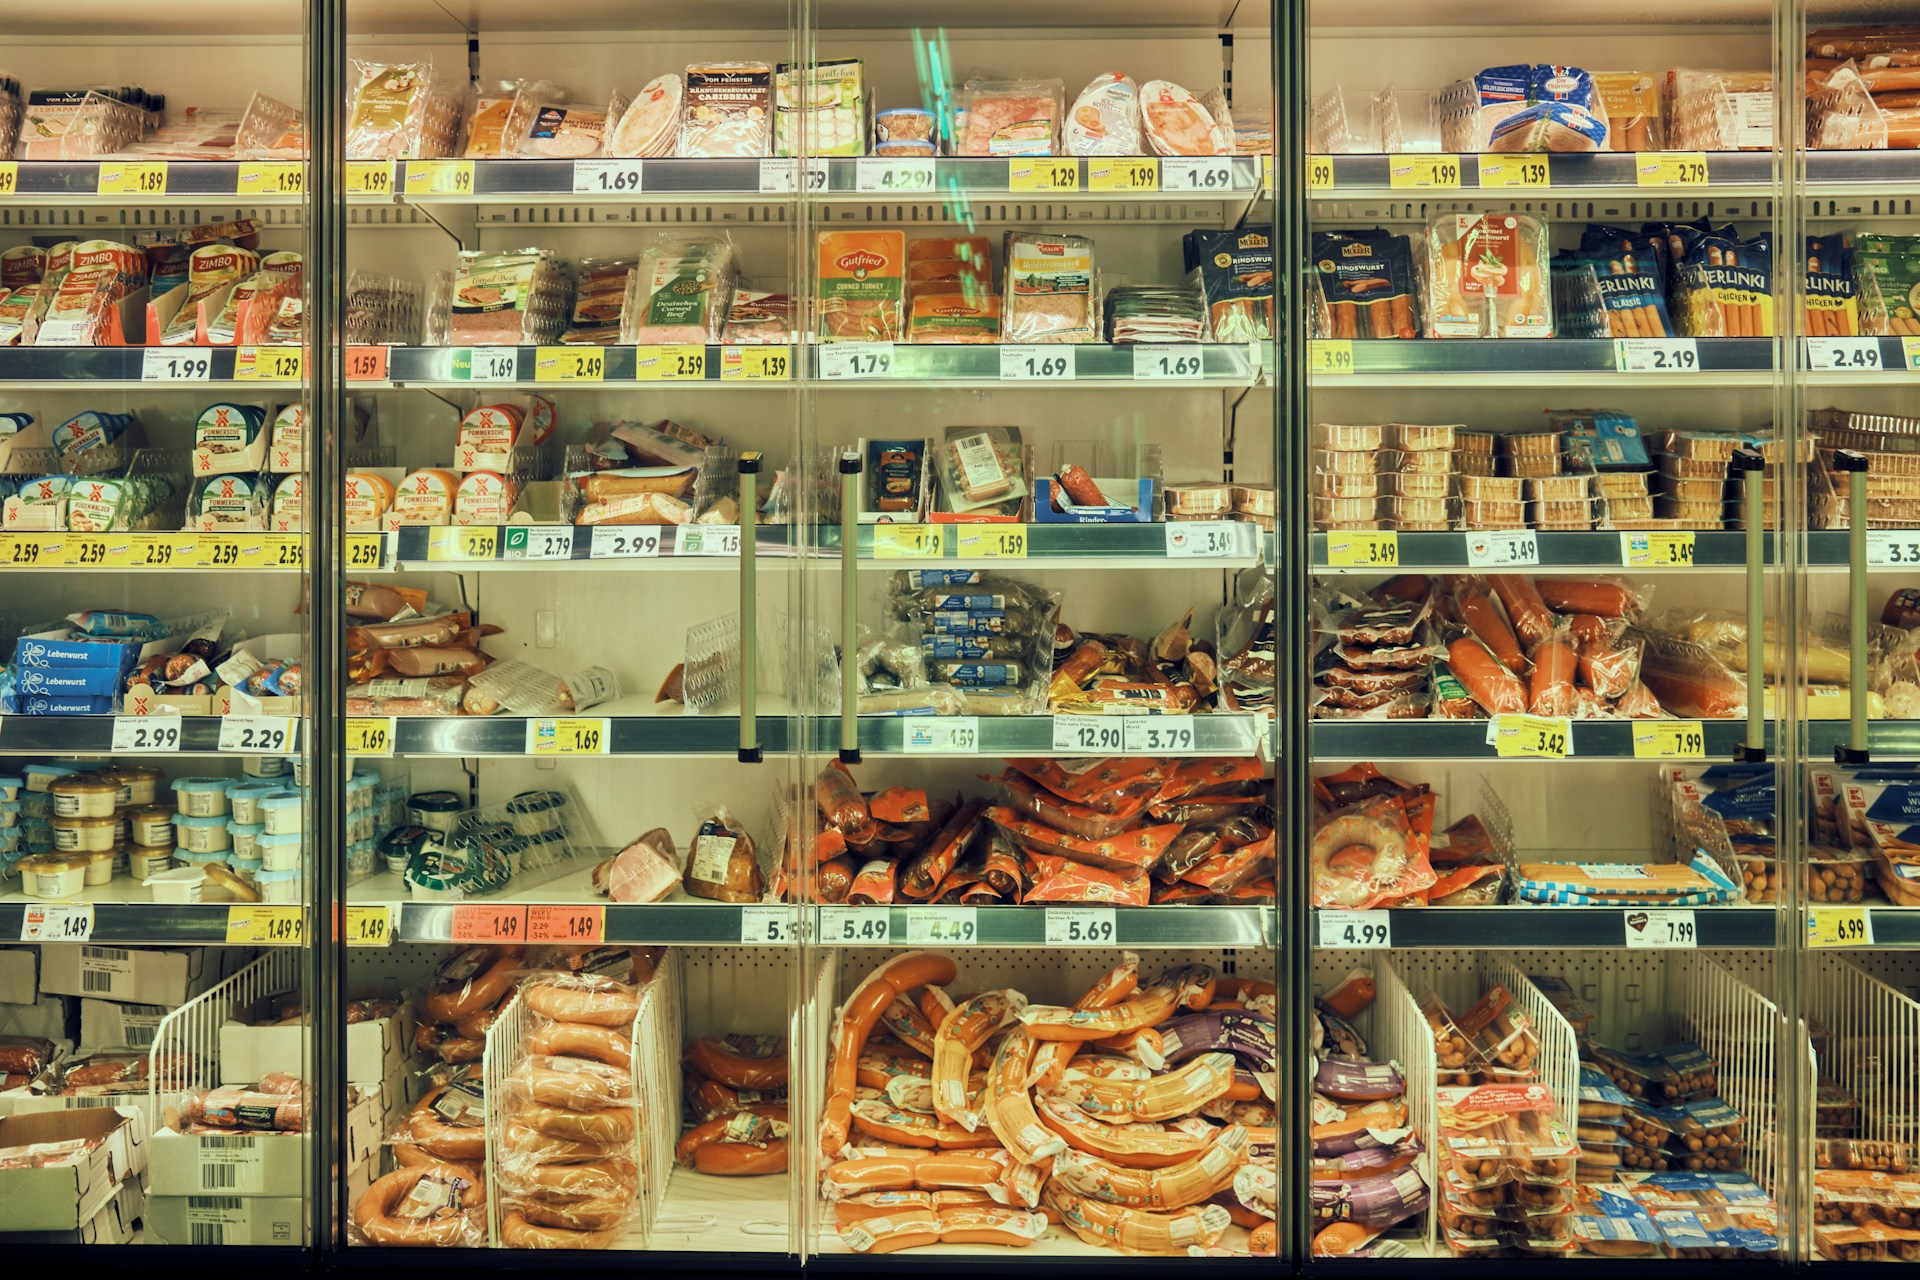
Investigators have identified a potential vulnerability involving refrigeration management systems supplied by Danish manufacturer Danfoss.
The company said affected equipment was running outdated firmware. It has reiterated that customers should update supported systems and migrate legacy equipment to current-generation solutions.
Cybersecurity firm Claroty previously identified vulnerabilities in Danfoss’s AK-SM 800A controller, including flaws that could potentially allow attackers to bypass authentication and execute code. However, investigators have not confirmed whether it was those specific vulnerabilities that were exploited in this particular incident.
Cybersecurity analyst Felix Aime of Sekoia Threat Detection and Research said Spain, Portugal, Poland, Germany and Belgium had also been affected by related incidents.
Dutch-Belgian retail group Ahold Delhaize separately reported a security incident affecting its network. However, no direct connection between that incident and the French supermarket attacks has been established.
With retailers increasingly depending on connected systems to manage refrigeration, energy use and other operations, the French attack is highlighting what could happen if those systems are compromised. The consequences of which could go beyond lost data to spoiled stock, business disruption and safety risks.
Security specialists recommend reviewing remote-access permissions, separating operational technology from corporate networks, updating firmware and ensuring that refrigeration systems can be safely managed if network access is compromised.